
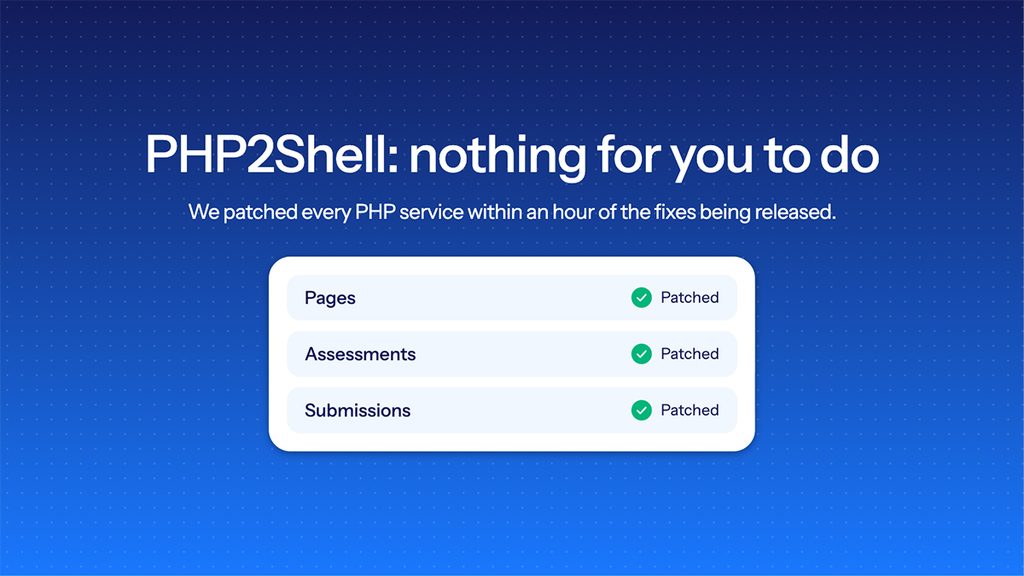
Good news: there’s nothing for you to do. We had every one of our PHP services patched and hardened within an hour of the fixes being released, and we’ve found no evidence that anyone tried to exploit the vulnerabilities. Your pages, assessments, and submissions are running as normal.
PHP2Shell is the name given to two critical PHP remote code execution vulnerabilities, CVE-2026-109618 and CVE-2026-109619, disclosed on 20–21 October 2026. PHP has released fixes in versions 8.5.12, 8.4.27, 8.3.36 and 8.2.35.
Did ScoreApp run an affected PHP version?
Yes, at the time of disclosure. Parts of the ScoreApp platform run on PHP, including the services behind pages, assessments and submissions, and they were on affected versions when the vulnerabilities were announced.
Are patches or protections in place?
Yes. We began assessing the vulnerabilities as soon as they were disclosed and prepared extra configuration hardening that closes the known attack path. On 21 October 2026, within one hour of the PHP patches being released, we deployed the patched versions to all our PHP services together with that hardening. Every ScoreApp PHP service now runs a fixed version.
Do I need to take any action?
No. ScoreApp manages the PHP services behind your pages, assessments and submissions, so nothing needs updating on your side.
Has any impact been identified?
No. We reviewed our server logs and firewall telemetry and found no evidence of exploitation attempts or successful attacks, and no impact on customer data or service availability.
If you have questions, contact ScoreApp support.